SOC 2 Type II · HIPAA · PCI DSS · ISO 27001 · FedRAMP

Compliance-Ready Colocation Providers: Verified Certifications, Not a Checkbox on a Brochure

A compliance-ready colocation provider can hand you current evidence, not a badge: a SOC 2 Type II report covering a recent 6–12 month period, a signed HIPAA BAA, a PCI DSS Attestation of Compliance and an ISO 27001 certificate with its scope and expiry date. Ask for each before a facility goes on your shortlist. Under 100 kW, plan on $225–250 per kW per month for space and power (October 2026 index), plus any cage build-out.

Updated November 2026 · Bob Spiegel, Founder, QuoteColo

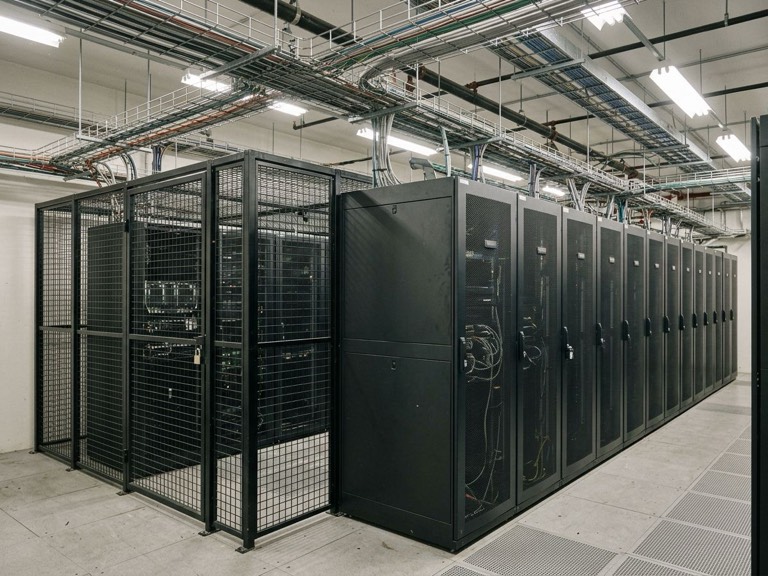
A locked wire-mesh colocation cage around server cabinets, with a card and biometric reader and a security camera
Bob Spiegel

“Tell me what you’re deploying; I’ll come back with real options from a network built over 20 years.”

— Bob Spiegel, Founder, QuoteColo

From our desk, November 2026

$225–250
per kW per month under 100 kW, space and power (October 2026 index)
$1,500–1,800
Full 48U rack, 5 kW, 1 Gbps, across the 26 markets on our sheet
$750–1,500
Half rack, 2 kW, the smallest footprint on our sheet

From Bob’s November 2026 price sheet and capacity list (listings, not confirmed offers) and the October 2026 price index (50+ provider responses). Prices are per month, space and power, unless noted.

The compliance frameworks that matter for colocation and what each actually requires

Most compliance problems come from buyers assuming a report or certificate exists, is current or covers their services, not from facilities lacking one.

FrameworkWhat it requires from the facilityWhat to check
SOC 2 Type IIMost often required for enterprise colocation. Audits 6–12 months of operation against up to five Trust Service Criteria.Type II, not Type I; when the period ends; the audit firm; which criteria are in scope
HIPAAThere is no official HIPAA certification. The facility typically covers its own physical safeguards; device and media controls and the rest usually stay with you.Whether it signs a Business Associate Agreement (BAA) and for which services (more likely needed with remote hands or media handling); its physical safeguard documentation; a SOC 2 Type II or HITRUST report covering physical controls
PCI DSSPhysical security (Requirement 9), network security controls (Requirement 1), secure systems and software (6) and access (7 and 8), assessed by a Qualified Security Assessor. For space and power, the provider usually covers Requirement 9; the rest stays with you unless it manages them.A current v4.0.1 Attestation of Compliance (AOC) covering your services; a responsibility matrix
ISO 27001A third-party audited standard with 93 controls. Certificates last 3 years, with annual surveillance audits.A current certificate to the 2022 version; a scope that covers your facility and services; the certification body (check it there or on IAF CertSearch)
FedRAMP / FISMAFedRAMP authorizes cloud service offerings, not buildings. A colocation facility supports federal workloads when a FedRAMP-authorized cloud service runs there and inherits its physical (PE) controls. FISMA is the underlying law, not a certification.Which FedRAMP-authorized services inherit the facility’s physical controls, at what impact level; a NIST SP 800-53 control mapping for the facility
HITRUST CSFIncreasingly required in healthcare and life sciences. Assessments come as e1 or i1 (valid 1 year) and r2 (valid 2 years); healthcare customers most often ask for r2.The assessment type (e1, i1 or r2); the expiry date; a scope that covers your facility and services

The five SOC 2 Trust Service Criteria are Security, Availability, Processing Integrity, Confidentiality and Privacy.

What to ask vs. what providers usually send

A claim on a website is not a document your auditor can use.

FrameworkWhat providers usually sendWhat you should ask for
SOC 2“We’re SOC 2 compliant” and an 18-month-old Type I reportThe current Type II report and the period it covers
HIPAAA web page that says “HIPAA compliant”A signed BAA template and the physical safeguard policy
PCI DSS“We support PCI DSS environments”The current AOC and its PCI DSS version
ISO 27001A certificate image on the websiteThe certificate with its expiry date and scope statement
FedRAMP“FedRAMP in progress” or “FedRAMP ready”The FedRAMP-authorized services that inherit this facility’s controls, and its NIST 800-53 physical-control mapping
HITRUST“HITRUST certified”The HITRUST certification letter and report: assessment type, expiry date and scope
Physical security“24/7 security and cameras”Log and footage retention periods, mantrap documentation and a visitor log audit trail
Audit support“We support audits”An audit contact, a documentation turnaround SLA and past audit support examples

We ask every provider for current compliance reports and certificates before it appears on your shortlist. Expired reports or certificates and marketing-language claims don’t pass the filter.

Want these numbers for your own deployment? and we’ll reply with the providers that fit, with their prices.

Cage vs. cabinet: why physical isolation matters for compliance

Most regulated organizations don’t need a full cage, but they do need access they can document.

Shared cabinet

  • Acceptable for most frameworks if cabinet access controls are documented and logs are available on request.
  • Can fall short for PCI DSS if people outside your team can reach in-scope systems, or where a healthcare policy requires private space.
Private cage

  • You control the access list; the facility logs entries.
  • Gives your auditor a clear physical boundary for HIPAA, PCI DSS and FedRAMP.
  • Half and quarter cages from mid-tier providers cost a fraction of a full cage and are easy to miss online.

Either way, your auditor will ask who can enter, how access is granted, revoked and logged, how long logs are kept, and whether in-scope systems are separated from the rest. For cage sizes and costs, see private cage colocation prices and services.

Physical security requirements: what auditors actually check

Auditors ask for the policies and logs behind the badge readers and cameras.

What auditors checkWhat the provider should be able to show
Access control documentationA written policy for provisioning and deprovisioning, scheduled access list reviews and tested emergency access procedures
Camera coverage and footage retentionThe areas covered and a stated retention period, at least three months where PCI DSS applies, not just “we have cameras”
Visitor and contractor access logsName, time in and out, escort and purpose, kept as long as your framework requires
Two-factor physical accessWhich layers (building, data hall, cage or cabinet) use badge plus PIN or biometric
Incident documentationA written process for failed access attempts, unauthorized entry and tailgating, with each incident investigated, remediated and recorded

Ask for the documents themselves, not a description of the hardware.

Regulated organizations QuoteColo matches to compliant providers

Organization typeYour compliance situationWhat you get from our shortlist
Healthcare / health techHIPAA physical safeguards, and a BAA where the facility’s role calls for oneFacilities that sign BAAs where their role calls for one, with SOC 2 Type II or HITRUST reports covering physical controls; cage options
Fintech / paymentsPCI DSS in scope; service providers that can affect your cardholder data environment supply an AOC or evidence for your assessmentA current AOC against the latest PCI DSS version, scoped to your deployment
SaaS with enterprise customersEnterprise contracts require SOC 2 Type II, and auditors ask about physical controlsCurrent SOC 2 Type II reports covering at least Security and Availability; documented audit support
Government / defense adjacentFedRAMP Moderate or High; a facility can’t be FedRAMP authorized on its own; what counts is the cloud services that inherit its controlsFacilities whose physical controls are inherited by FedRAMP-authorized services at your impact level, with a NIST 800-53 mapping
Life sciences / pharmaHITRUST or 21 CFR Part 11, GxP validation documentation and stricter audit trailsA HITRUST r2 assessment and experience with GxP documentation requests
Enterprise SaaS, ISO 27001 requiredCustomer contracts require ISO 27001 from infrastructure providersCurrent ISO 27001 certificates scoped to your deployment, with surveillance audit history

Why “compliance-ready” is the most misused phrase in colocation

Every provider says it’s compliant. Most buyers find out what that means when the auditor asks for the documents.

THE DIY WAY

You search for HIPAA compliant colocation providers

They all claim HIPAA compliance. HIPAA has no certifying body, so a facility can make that claim without a third-party audit or a BAA process.

THE DIY WAY

You ask for their SOC 2 report

They send a Type I report from 18 months ago. Type I shows controls were designed correctly on one day. Type II tests how controls worked over a period, usually 6–12 months; enterprise customers and their auditors usually ask for it.

THE DIY WAY

You visit the facility and it looks secure

You see mantraps, cameras and badge readers. The tour doesn’t show whether access logs are auditable, footage retention meets your framework or any of it is in a form your auditor can use.

How it works

You send the specs. We find the options. You decide.

STEP 1

Send your requirements.

Tell us what you're deploying, where you want it, and when you need it. Send the specs you have; we'll help with the rest.

HardwareRacks & kWLocationStart date

Estimates are fine. No perfect RFP needed.

STEP 3

Take the next step. On your terms.

Like the options? Contact the providers directly. Need more detail? Call or email us. We're here to help, not push you.

  • Go directly to the providers you like
  • Ask us questions whenever you need

Get Compliance-Ready Colocation Options

Free for buyers

Your price is the same as going direct.

All-in estimates by email

From 500+ providers. No sales calls, no long forms.

Trusted service since 2004

5,000+ clients helped.

Your request will be sent securely to QuoteColo.

Compliance-ready colocation going into 2027: what’s changed

Report dates matter.

A SOC 2 report whose period ended in 2022 has missed three or four annual cycles. We check the dates, not just that a report exists.

“Compliance-ready” is not “compliance-certified.”

“Ready,” “capable” and “friendly” all mean the facility hasn’t completed the audit or assessment. Your auditor needs controls that have been tested.

AI in regulated industries adds new requirements.

Healthcare AI, fintech ML and government AI workloads are landing in facilities that weren’t built for compliance-sensitive GPU deployments.

Compliant deployments can be smaller than you think.

Quarter and half cages with current SOC 2 Type II reports exist in most major markets. Teams with 1–6 racks rarely find them through standard search.

Case studies

See how we helped teams secure colocation with the right power, pricing, and providers.

Leonard Roszkowski

CEO Elemental Energy Solutions

Problem: Needed to source ASIC servers domestically. Skeptical about working with a new organization.

What we did: Connected them to buyers, sellers, and infrastructure partners across deployments. Removed procurement and logistics overhead entirely.

Result: Rapid organizational growth in a short period. Now uses QuoteColo as an ongoing procurement interface across hardware and infrastructure.

Noel Frutasio

CEO FSN Services and Communications

Problem: Regularly needed colocation space across multiple US states and time zones. Difficult to navigate the market without deep industry knowledge.

What we did: Defined requirements in one meeting, then delivered proposals with multiple carrier and data center options across every target market.

Result: Placed in 4 cities. Contracts signed quickly. Multi-state colocation needs resolved through a single point of contact.

Tim Mandell

DC Mining / MDI Access

Problem: Needed reliable options for crypto mining containers and equipment, along with industry partners who could support real deployment requirements.

What we did: Connected the project with relevant mining infrastructure and equipment resources through the QuoteColo network, simplifying the search and evaluation process.

Result: Gained a clearer path to suitable mining infrastructure, equipment and industry contacts without having to source every option independently.

5,000+

Clients helped since 2004

No Cost

to Buyers

500+

Worldwide providers

Quotes

in 48 h

FAQ: compliance-ready colocation

What’s the difference between SOC 2 Type I and SOC 2 Type II for colocation?

SOC 2 Type I is a point-in-time assessment. It documents that controls were designed correctly on a specific date. SOC 2 Type II covers an operational period (typically 6–12 months) and audits whether controls actually functioned correctly over time. For most compliance purposes (enterprise customer contracts, healthcare, financial industry requirements) Type II is required. Always ask for the Type II report and confirm the period covered is recent.

Is HIPAA compliance something a colocation facility can be certified for?

No. HHS doesn’t recognize any HIPAA certification, so a facility can’t be ‘HIPAA certified’. What matters is whether the provider signs a Business Associate Agreement (BAA) where its role calls for one (more likely when remote hands, media handling or managed services touch your systems; ask your counsel), and whether it documents physical safeguards against the Security Rule (§164.310), ideally in a SOC 2 Type II or HITRUST report. Each organization does its own risk analysis.

What does PCI DSS compliance mean for a colocation facility?

A PCI DSS compliant colocation facility has been assessed as a service provider against the PCI DSS standard and holds an Attestation of Compliance (AOC) from a Qualified Security Assessor (QSA). The current version of the standard is PCI DSS v4.0.1. Ask for the AOC directly, check which version it was assessed against, and check whether the facility is listed on Visa’s Global Registry of Service Providers or Mastercard’s list of compliant service providers.

Do I need a private cage for compliance, or is a shared cabinet acceptable?

It depends on your framework and auditor: for most SOC 2 and ISO 27001 requirements, a shared cabinet with documented access controls is acceptable. For PCI DSS environments that require physical separation between in-scope and out-of-scope systems, a private cage is the cleaner posture. For FedRAMP High workloads, expect the agency or cloud provider to require dedicated, documented physical isolation. Half-cage and quarter-cage options give compliance-grade isolation at smaller footprints, and we include them when they fit.

How do I verify a colocation facility’s ISO 27001 certificate is current?

ISO 27001 certificates are issued for 3 years with annual surveillance audits. Ask for the certificate document. It shows issue date, expiry date, scope, and certifying body. You can verify directly with the certifying body (BSI, Bureau Veritas, DNV, etc.) or check the IAF CertSearch database. A certificate that can’t be independently verified is worth treating with caution.

What physical security documentation should I request before signing a colocation contract?

The documentation your auditor will actually request: (1) access control policy including provisioning/deprovisioning process and review schedule; (2) camera coverage map and footage retention period; (3) visitor access log policy and retention period; (4) physical security incident response procedure; and (5) the most recent physical security audit or penetration test report. Request these before the site visit, not during it.

Can QuoteColo find compliant colocation for small deployments (1–6 racks)?

Yes: mid-tier and regional operators with current compliance reports and certificates often accept 1–6 rack footprints, as a quarter cage, a half cage or 2–6 racks. Tier 1 operators typically want enterprise-scale commitments, and the smaller options rarely show up in standard search. Send your framework and footprint once, and we ask matching providers for current compliance reports and certificates before they make your shortlist.

What’s the difference between a compliant facility and a compliance-ready facility?

A compliant facility has completed third-party audits and holds current reports and certificates (a SOC 2 Type II report, a PCI DSS AOC, an ISO 27001 certificate) with documentation available on request. A ‘compliance-ready’ facility believes its infrastructure could support compliant workloads but has not completed the audits or assessments. Your auditor needs documentation of controls that have been tested, not controls that could theoretically be tested.

Get 2–4 qualified options in 48 hours

Free for buyers

Your price is the same as going direct.

You will get all-in price estimates by email

From 500+ providers. No sales calls, no long forms.

Trusted service since 2004

5,000+ clients helped.

Your request will be sent securely to QuoteColo.